Security that removes blockers, not just risk
Every interaction we handle carries your brand. The security infrastructure behind it carries your data. We protect both with enterprise controls, independently verified certifications, and a security-first culture that runs through every team, every process, and every operation.
Why security matters at Otonomee
Remote-first. Global scale.
As a remote-first operator with team members across multiple continents, handling sensitive and often complex customer interactions every day, we enact enterprise-grade security policies. It isn't something we bolt on; it's embedded into how we hire, how we train, how we access systems, and how we respond when things don't go to plan.
When you partner with Otonomee, you're trusting us with your customers, your data, and your reputation. That's a responsibility we take seriously at every layer — people, process, and technology.




Our security credentials
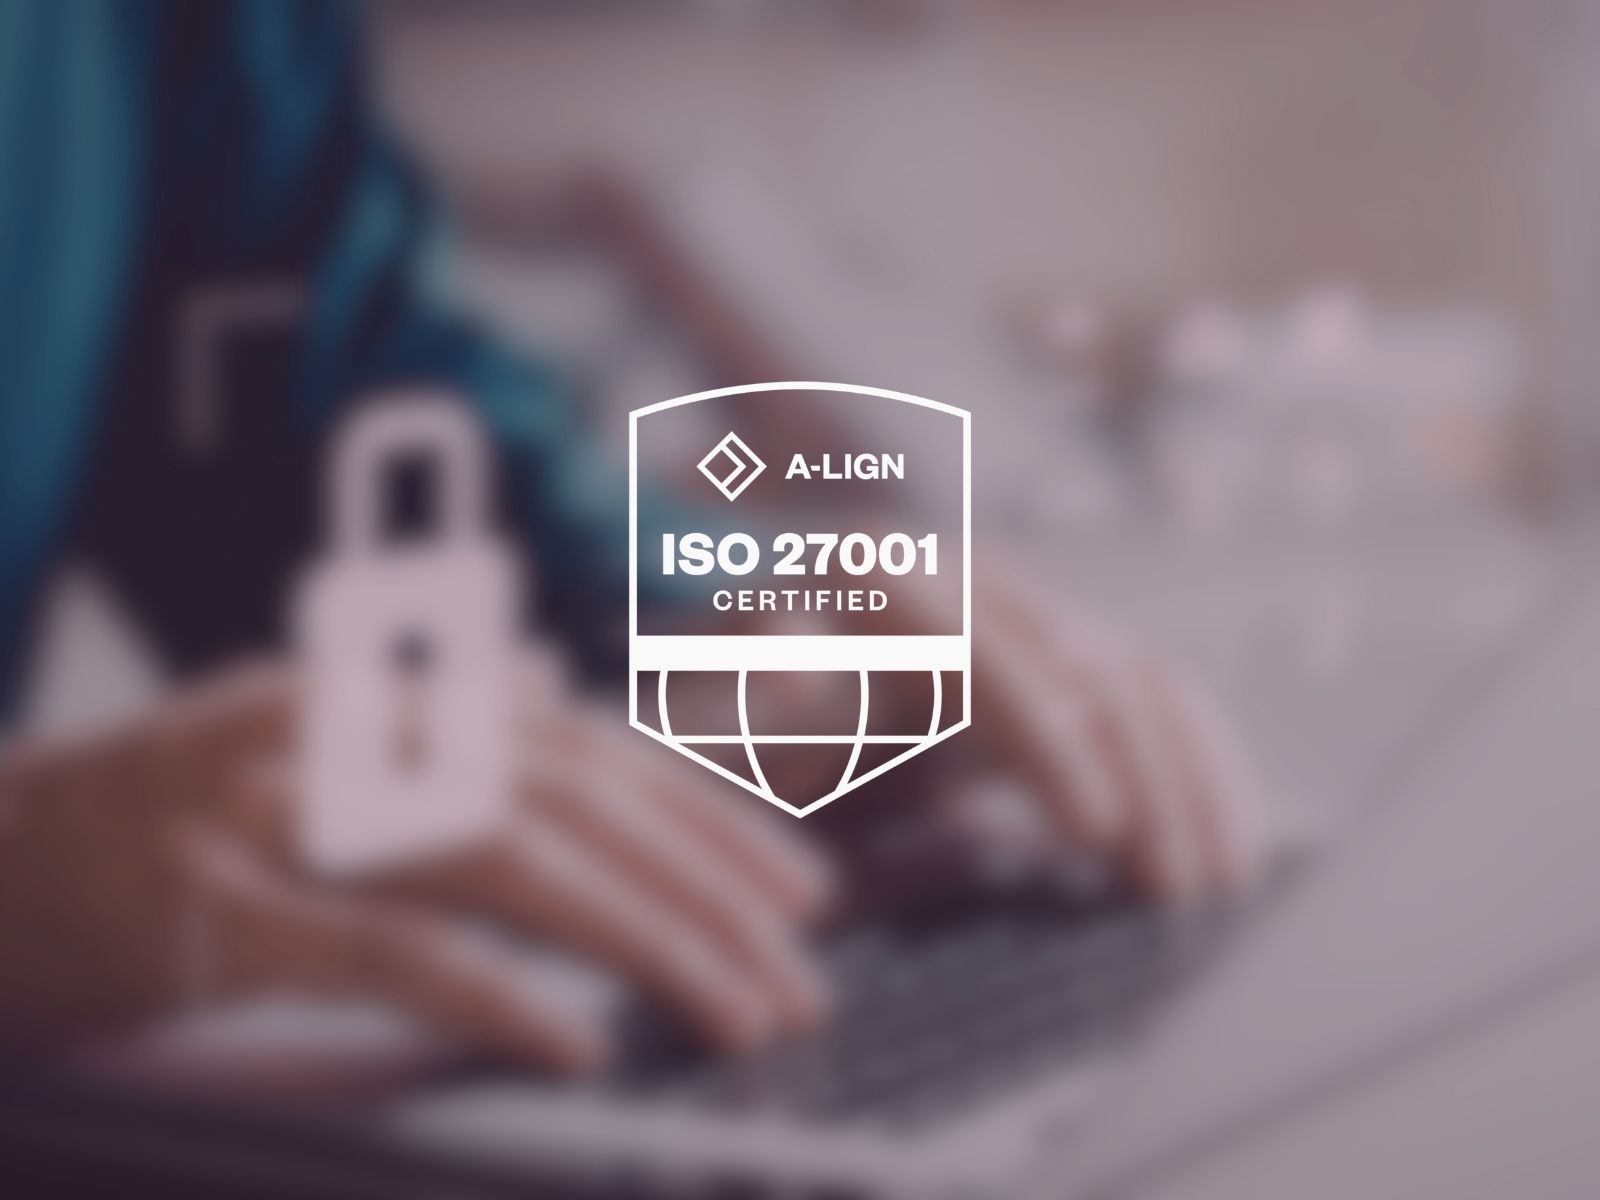
ISO/IEC 27001:2022
PCI DSS v4.0.1 Service Provider
HIPAA Compliant
GDPR Compliant
SOC 2 Type II Certification in Progress
85%+ retention. Our people stay for the long term, so the same trained, trusted hands are always on your data.
5+ certifications: ISO 27001, PCI DSS, HIPAA, SOC 2 Type II, GDPR and more — maintained across every operation.
4 continents. One security framework applied consistently, regardless of where your team operates.
Over 1,000,000 customer touchpoints handled annually, every one protected by the same controls and protocols.
Controls you can count on
Our security infrastructure is designed to protect data at every point, from how it enters our systems to how it is accessed, used, monitored, and stored.
All data is encrypted in transit using TLS 1.2/1.3 and at rest using AES-256. Whether data is moving between systems or sitting within them, it is protected by the same standards required by the enterprise clients we serve.
Role-based access management, multi-factor authentication, and Zero Trust principles ensure that only authorised team members can access the data they need - and nothing more. Controls are enforced consistently across all team member environments, regardless of location.
24/7 real-time security monitoring, anomaly detection, and automated alerting give us continuous visibility across our operations. Threats are identified and escalated before they can impact our clients or their customers.
Defined incident response plans, tested through regular tabletop exercises, ensure we act fast, communicate clearly, and recover effectively. Clients are notified promptly in line with contractual and regulatory obligations, with full post-incident review and remediation steps shared as standard.
Our security posture is verified through independent external audits - including quarterly penetration testing and vulnerability scanning, ISO 27001:2022 surveillance audits, and QSA-led assessment under PCI DSS v4.0.1. We don't wait for clients to ask; we maintain the evidence before the question is raised.
Security built for the complexity our clients face
Our security posture isn't a checkbox. It's the infrastructure that makes it possible to handle sensitive, high-stakes customer interactions on behalf of high-growth and enterprise-grade brands, at scale, without compromise.

For enterprise clients

For tech and scale-up partners

For your end customers
Frequently asked questions
Our infrastructure runs on enterprise-grade cloud platforms with geographic redundancy and data residency controls built in. We support jurisdiction-specific data storage requirements Speak to our team for a full breakdown relevant to your region and compliance obligations.
All client data is logically segregated at the system level using separate, isolated environments. Data belonging to one client is never accessible to another - by architecture, not just by policy.
Our Incident Response Plan activates immediately upon detection, with defined escalation paths and client notification obligations built in. You are informed promptly, in line with contractual and regulatory requirements. We conduct a full post-incident review and share findings and remediation steps - not just a summary.
Yes - and beyond what certification requires. ISO 27001:2022 mandates annual surveillance audits; we supplement these with quarterly vulnerability scanning, annual penetration testing, and an ongoing QSA-led assessment under PCI DSS v4.0.1. We are currently completing our SOC 2 Type II audit — contact us for current status.
A remote-first model doesn't weaken security - when implemented correctly, it strengthens it. Without a network perimeter to rely on, every access decision is explicit. We operate on Zero Trust principles: strict access controls, MFA enforced across all environments, managed devices, encrypted connections, and continuous monitoring regardless of where a team member is located.